Registry approval is not permission to run
AWS Agent Registry makes approved resources discoverable. Runtime access remains a separate decision backed by separate credentials.
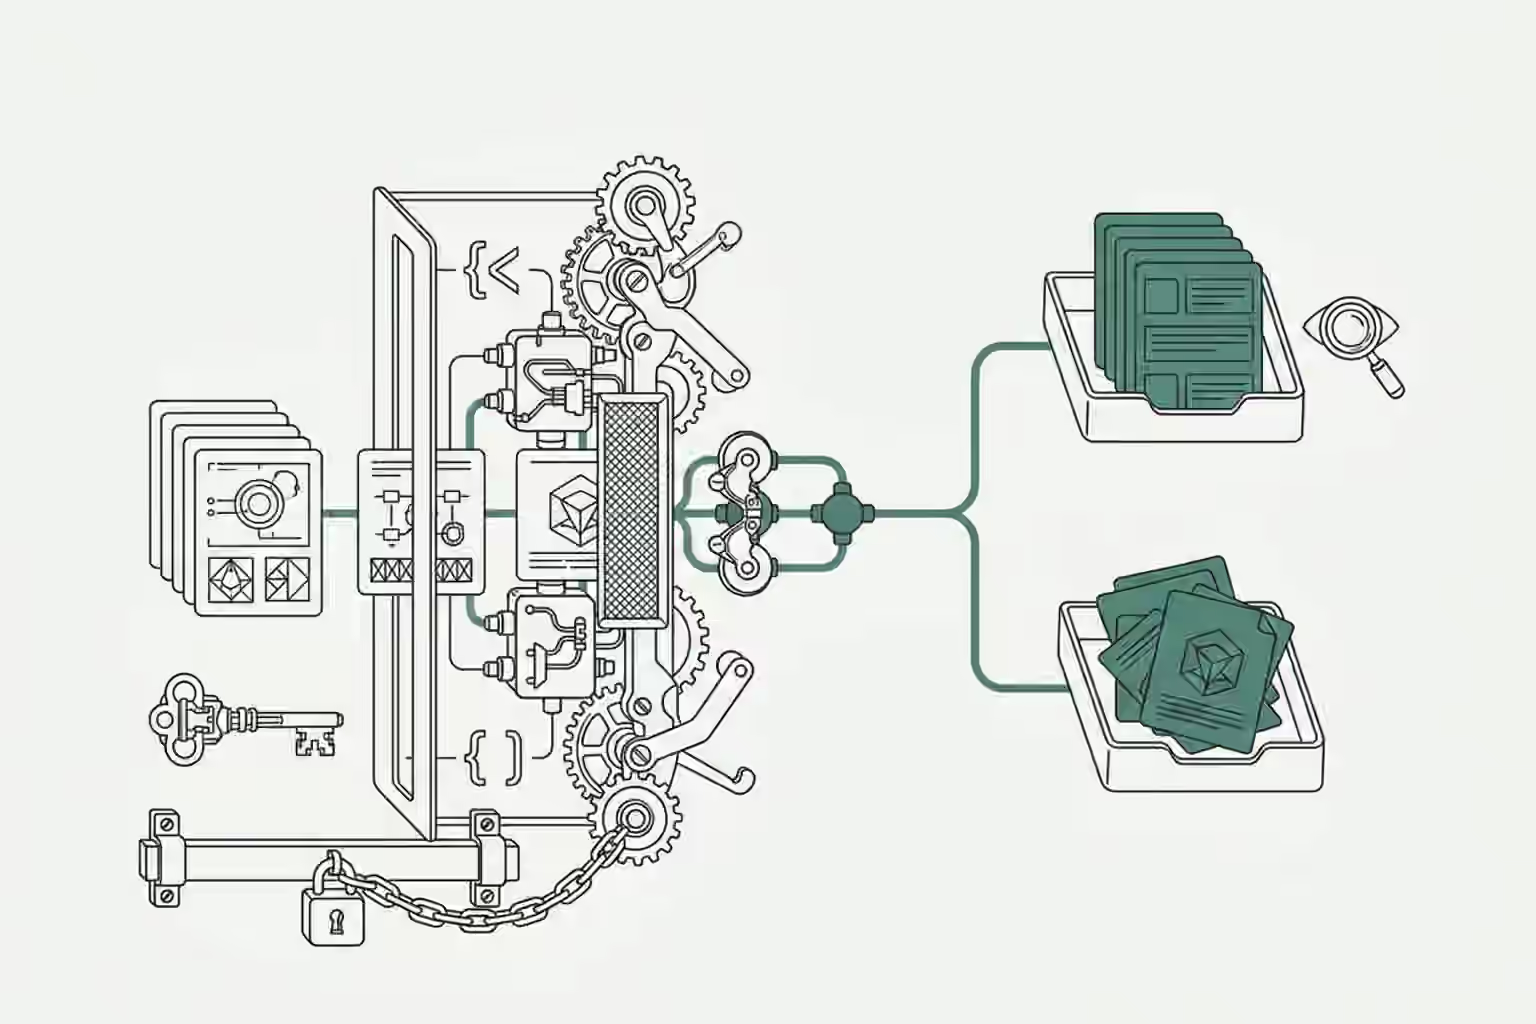
AWS says registry approval controls discovery. AWS says a caller needs separate credentials to run the resource. That division is explicit enough to test.
AWS released Agent Registry for general use on August 31, 2026. AWS describes it as a private, governed catalog and discovery layer for agents, tools, skills, MCP servers, and custom resources.
A registry is a controlled list of available software. Lifecycle means the states from submission through retirement. Neither definition gives a catalog record authority over the software it describes.
Five states control the record
AWS documents five record states: DRAFT, PENDING_APPROVAL, APPROVED, REJECTED, and DEPRECATED.
AWS assigns each state change to a named role:
- AWS says a publisher creates or updates a record in
DRAFT, then submits it intoPENDING_APPROVAL. - AWS says an approver approves or rejects the pending record.
- AWS says a curator moves an unneeded record into
DEPRECATED.
AWS also says auto_approve can move a submitted record directly into APPROVED. An automated route changes who performs the approval step. It does not expand what approval means.
Approval changes discovery
AWS says only records approved by an administrator or curator appear in the discovery view. AWS says draft, rejected, and shadow resources remain outside that view. Approval therefore decides what discovery returns.
AWS documentation describes the same boundary. AWS says consumers search or browse the approved-record catalog to find resources. A result establishes that the organization made the record available for discovery.
AWS says discovery returns endpoint addresses and authorization details. AWS still requires the developer to request access and receive separate endpoint credentials. AWS says the caller uses those credentials to make authenticated calls to the resource.
That sequence leaves two records to inspect. A registry record shows why the resource appeared. An access record shows why this caller could run it.
Keep both decisions visible
A discovery test should check AWS’s rule that only approved records appear in discovery. An access test should check AWS’s requirement that a caller needs separate endpoint credentials to make authenticated calls. One passing test says nothing about the other decision.
AWS supplies the public evidence for this analysis. AWS is neither a Muniment customer nor an endorser.
Sources
- AWS: Manage agents, tools and skills at scale with AWS Agent Registry aws.amazon.com
- AWS: AWS Agent Registry is now generally available aws.amazon.com
- AWS Agent Registry documentation docs.aws.amazon.com