A policy compiler checks structure, not intent
AWS shows where natural-language policy authoring stops: validation checks structure and tool names, while a person must confirm intent.
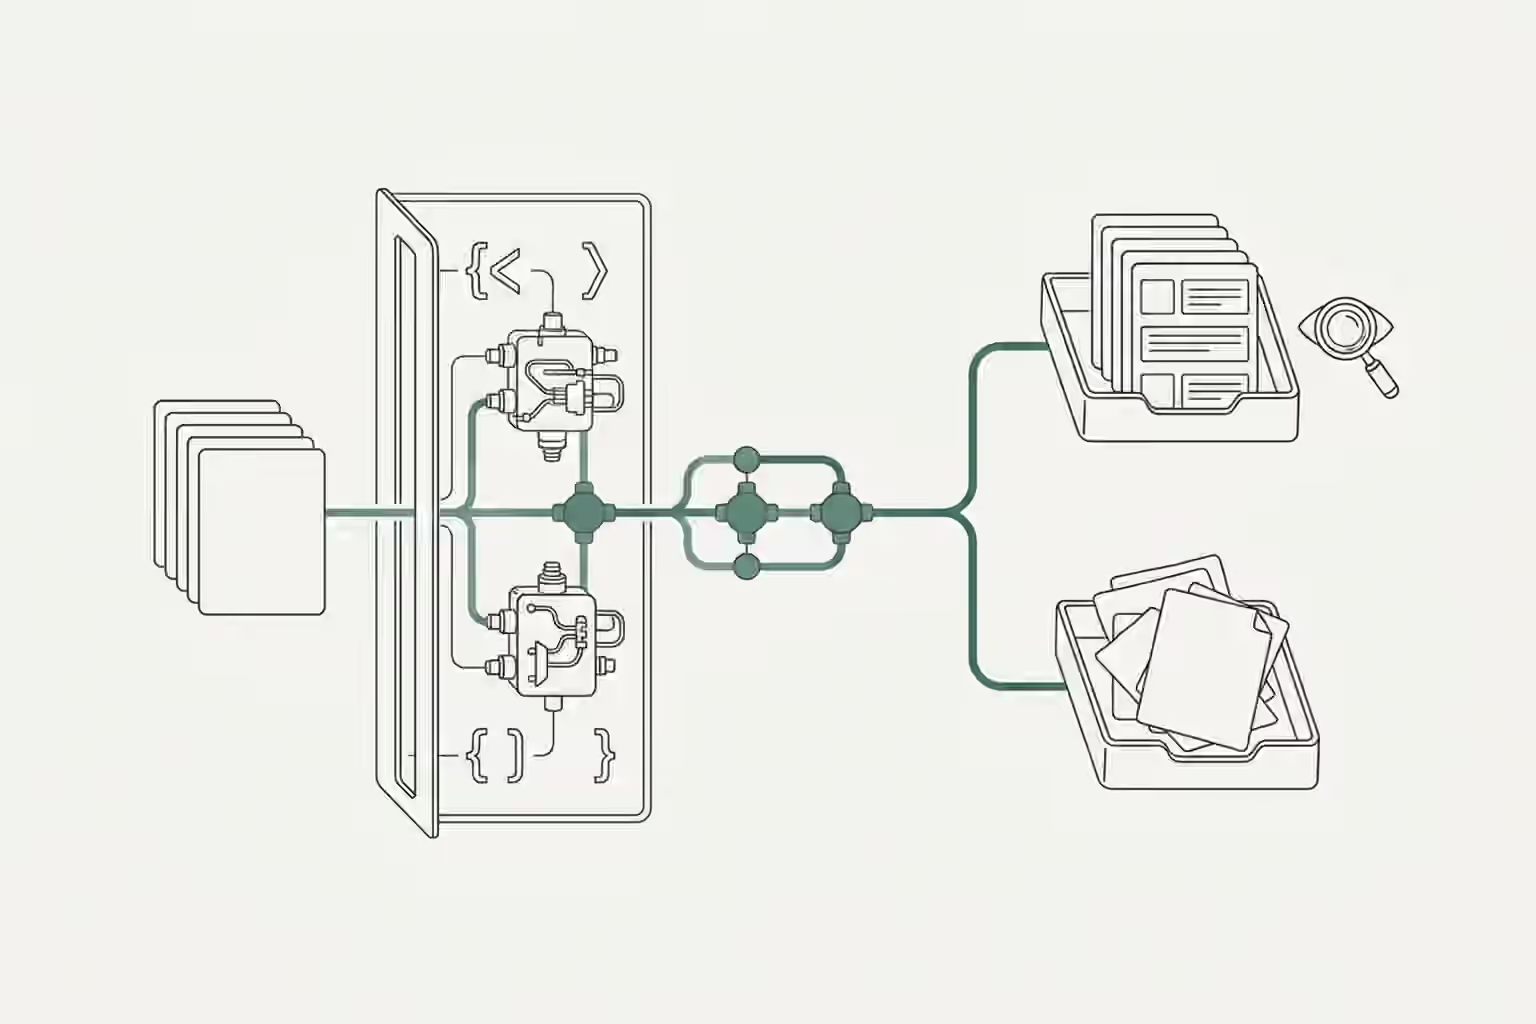
A policy compiler can reject malformed policy and still approve the wrong policy. AWS states that distinction in Policy Authoring for Amazon Bedrock AgentCore. Structure belongs to the compiler. Intent stays with the person who owns the rule.
AWS says its tool turns written rules into Dogwood policies that govern agent tool calls. Dogwood is an open policy language for expressing and enforcing those controls.
Model Context Protocol, or MCP, is a standard for connecting tools. AWS says Policy Authoring reads its tool manifest for exact tool names, arguments, and return values. Generated policy then uses the tools available through the AgentCore Gateway.
Supported rules reach beyond one tool call
AWS shows policies for argument limits and business-hour windows. Its examples also cover prerequisites, cumulative caps, and rate limits. These rules can inspect events from the current session.
Free-form text gets a separate check. AWS shows a generated policy that calls Amazon Bedrock Guardrails on a dispute description. The policy then compares the returned confidence score with a threshold.
Those examples matter because the input document must settle details that code cannot infer safely. AWS advises authors to name the time window, event key, threshold boundary, and whether a rule covers an attempt or outcome.
A cumulative cap shows the risk. AWS translates “transferred” as attempted transfers because the rule omits attempts and successful outcomes. The source says stating that choice in the document removes the guess.
Validation proves a narrower fact
AWS describes a four-step pipeline. It splits compound prose into atomic rules, routes expressible rules, translates them, and validates each candidate.
The final check has clear authority. AWS says the Dogwood compiler determines whether a policy parses and whether every name exists in the supplied schema. Failed candidates can return for limited translation rounds with the compiler diagnostics.
A valid name proves that the policy refers to a real tool or field. A valid expression proves that the language can parse it. Neither result proves that “attempt” should replace “outcome” or that a boundary includes the third action.
AWS therefore tells users to review each generated policy beside its source sentence. Under AWS’s process, a person must still confirm that the compiled policy matches the written rule. AWS states that validation cannot establish what the author meant.
Set-aside rules preserve the boundary
AWS says Policy Authoring sets aside rules that Dogwood or AgentCore Policy cannot enforce. The source names four types:
- AWS sets aside a principle without a condition on an action, field, or principal.
- AWS sets aside a request to change data, such as redaction, when the engine can only permit or deny a call.
- AWS sets aside a rule outside Dogwood’s expressions, such as weekend or federal holiday restrictions.
- AWS sets aside a rule outside session enforcement, including a cumulative cap across concurrent sessions.
AWS says the output keeps validated policies separate from atomic rules that were set aside. The routing step keeps an inexpressible rule from becoming valid syntax with different meaning.
AWS and its services are neither Muniment customers nor endorsers. The AWS post supplies public evidence for a strict operating rule: give compiler output authority over structure, never author intent.
Sources
- AWS: Authoring Dogwood policies from natural language in Amazon Bedrock AgentCore aws.amazon.com
- Model Context Protocol Specification modelcontextprotocol.io